

 Buy a Licensed Company
 Explore VASP Data
 Talk to an Expert

 Dren Hima
 is Head of Research at Coincub, leading research across digital asset regulation, licensing, market structure, tokenization and institutional adoption.
Outsourcing Crypto Compliance Is a Staffing Decision
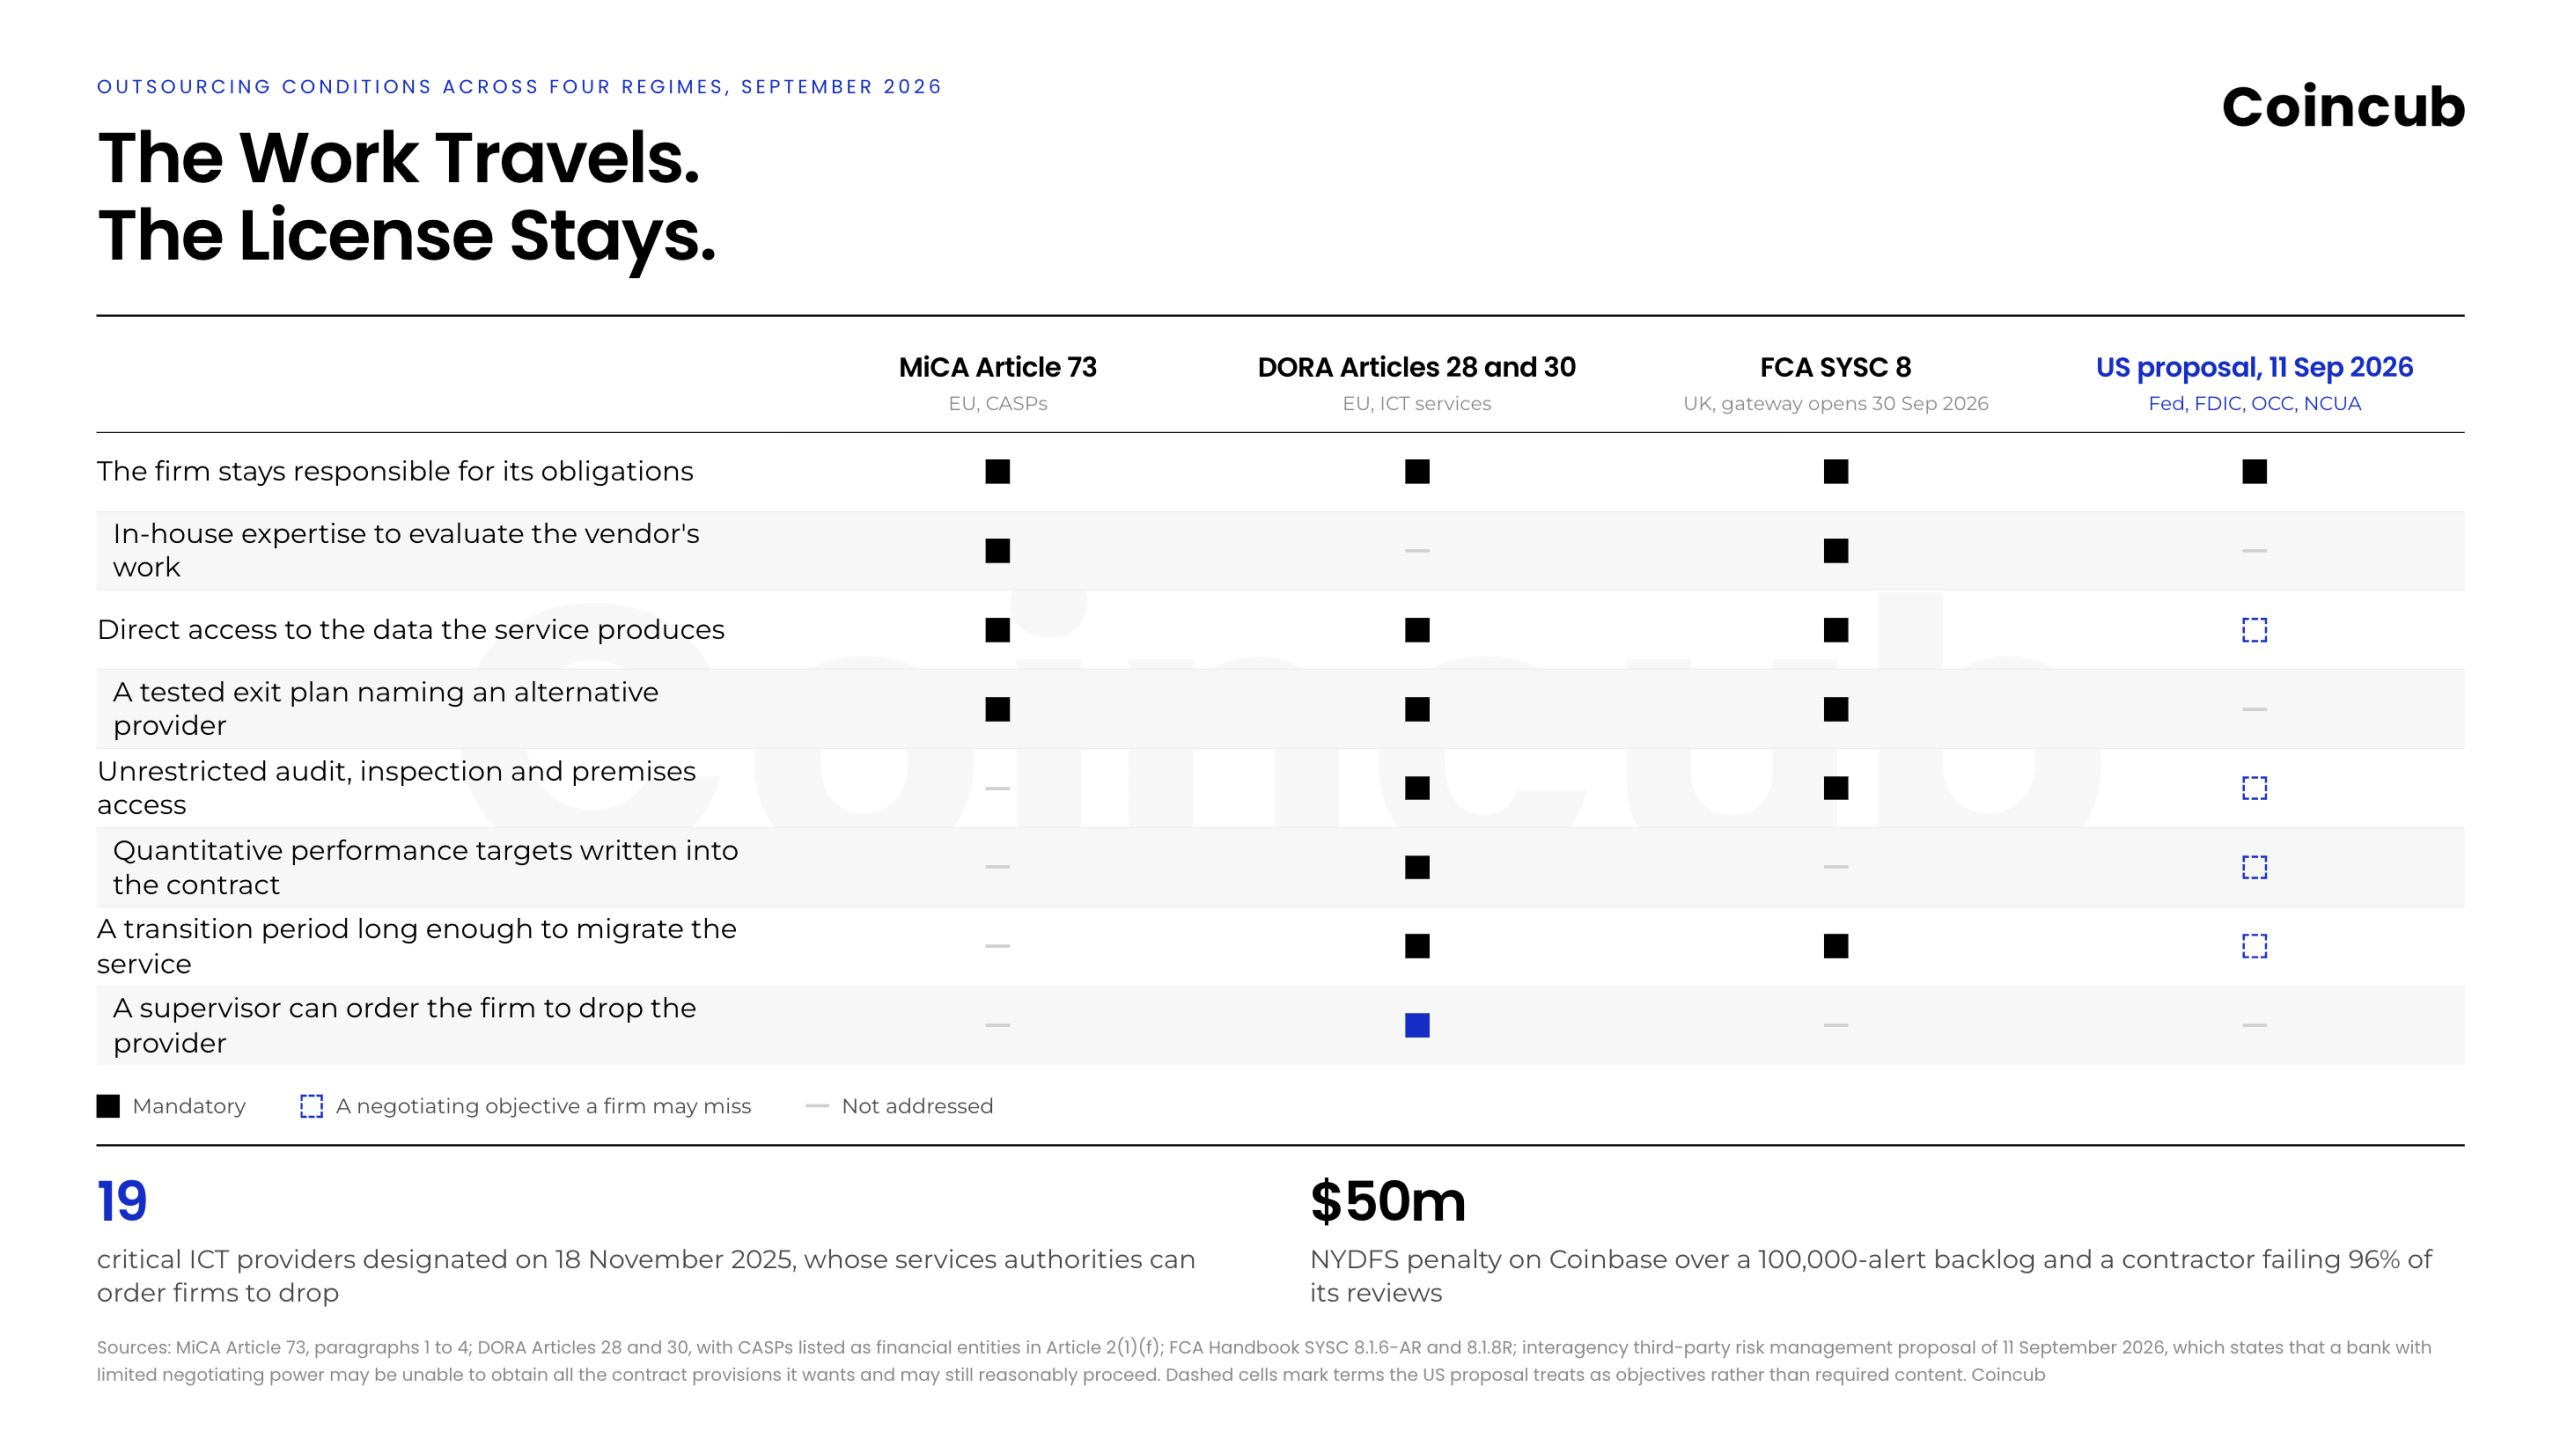
- MiCA Article 73 and FCA SYSC 8.1.8R both require an outsourcing firm to keep in-house expertise for evaluating the vendor’s work.
- A European CASP carries MiCA and DORA at once, and Article 73 compliance settles nothing under DORA.
- Supervisors can order a firm to drop a designated critical ICT provider.
- Washington proposed replacing the 2023 US third-party guidance on 11 September 2026 with a lighter, more tailored version.
- NYDFS fined Coinbase $50 million over a monitoring backlog of more than 100,000 alerts and a contractor that failed 96% of reviews.
Every crypto outsourcing agreement includes a sentence stating the firm remains responsible for its regulatory obligations. Regulators wrote that sentence first. MiCA carries it, DORA carries it, the FCA Handbook carries it, and the US banking agencies carry it. Putting it into a contract costs nothing and proves nothing.
Article 73 of MiCA requires a crypto-asset service provider that outsources an operational function to keep the expertise and resources needed to evaluate the service’s quality and manage the risk within it. The FCA imposes a matching condition on the firms under SYSC 8. Both conditions are about staffing. They ask whether the firm employs people who can read a vendor’s rule configuration, reproduce an alert decision, and price a key-recovery failure.

What MiCA Article 73 requires a CASP to keep in-house
Article 73 runs to four paragraphs and creates more work than its length suggests. The first sets the conditions on any outsourcing. The arrangement cannot reduce the provider’s responsibility, change its relationship with clients or its obligations to them, or alter the conditions of its authorization, and the third party must cooperate with competent authorities. Two further conditions in the same paragraph are the ones a supervisor can test on site. The provider retains the expertise to assess the outsourced service and direct access to the information it generates.
A CASP that cannot pull its own case files, rule versions, screening logs, and customer records out of a vendor platform without asking the vendor to run the query has not satisfied paragraph 1. Export rights, data formats and query access cost less to negotiate before signature than to retrofit during an inspection.
Paragraph 2 requires a written outsourcing policy covering contingency plans and exit strategies, scaled to the services being outsourced. Under paragraph 3, the written agreement must set out both sides’ rights and obligations and reserve a termination right for the CASP. Paragraph 4 obliges the CASP and the third party to hand authorities whatever they request to verify compliance. A vendor contract that routes regulator requests through the vendor’s legal team, or that treats rule logic as proprietary and off-limits, fails against paragraphs 1 and 4 together.
Custody technology, screening engines, blockchain analytics, identity verification, hosting and case management are all outsourceable under MiCA. The permissions on the CASP authorization still belong to the firm that holds them.
DORA contract terms for critical or important functions
Crypto-asset service providers authorized under MiCA are listed as financial entities in DORA Article 2(1)(f), so a European CASP operates under both instruments. DORA Article 28 repeats the full-responsibility principle and then adds machinery MiCA does not contain. Entities maintain a register of information covering every contractual arrangement for ICT services, at entity level and at consolidated level, and report annually on new arrangements, provider categories and the functions being supplied. Before signing, they assess whether the arrangement supports a critical or important function, whether it creates ICT concentration risk, and whether the provider is suitable. For critical or important functions, they document and test an exit plan that names an alternative and covers secure data transfer.
Article 30 then dictates contract content. Every ICT contract names the functions and services and states whether subcontracting is allowed and on what terms. It identifies the countries where services are delivered and data is processed. It guarantees data access and return in the event of insolvency or termination, and it sets service levels. The provider has to assist with incidents at no extra cost or at a price agreed in advance. Cooperation with competent and resolution authorities and notice periods for termination close the general list. Contracts supporting critical or important functions carry more. Performance targets must be both quantitative and qualitative. The provider must participate in threat-led penetration testing. The firm and its supervisors have unrestricted rights to inspect, audit, and access documentation. The contract also sets a transition period long enough to migrate the service elsewhere.
Compliance with Article 73 doesn’t address any of this. The two instruments cover overlapping subject matter with different tests, and a CASP register entry does not signal DORA readiness to anybody who reads both.
Critical ICT provider designation and forced termination
DORA also reaches past the regulated firm. On 18 November 2025, the European Supervisory Authorities designated 19 critical ICT third-party providers, among them Amazon Web Services, Microsoft, Google Cloud, Oracle, SAP, IBM, Accenture and Bloomberg. Designation brings each under the direct oversight of a lead overseer, with annual fees and an EU coordination point.
A lead overseer assesses the provider’s risk management and governance, issues recommendations where it finds gaps, and can publish a provider’s non-compliance. As a final step, authorities can require financial entities to suspend or terminate their use of that provider’s services.
Read that against the exit plans in Article 28. The trigger for executing one may be a supervisory decision about a vendor, taken by an authority the firm does not answer to, on a timetable the firm does not set. A CASP running identity verification, analytics, and case management on one hyperscaler has a concentration problem it cannot price from its own contract. The designation list is also a map of shared infrastructure. Four compliance vendors procured separately, from four different sales teams, on four different renewal cycles, can still sit on the same cloud region and the same designated provider. The same names turn up again in AI agent deployments across European crypto firms, since model hosting and compliance tooling tend to land with one supplier.
SYSC 8 conditions and the UK authorization gateway
Britain ships the same principle with a longer checklist. SYSC 8.1.6-AR states that a common platform firm outsourcing critical or important operational functions remains fully responsible for discharging its obligations. The arrangement cannot delegate senior management responsibility, change client relationships or undermine the conditions of authorization. SYSC 8.1.8R then sets twelve conditions on top. The provider needs the ability, capacity and any authorization the work requires. It must perform effectively and lawfully, supervise the function, manage the risk, and disclose anything that materially affects its performance. The firm must supervise the arrangement, have the expertise to do so, and act when the provider underperforms.
Two of the twelve absorb most of the negotiating time. The firm needs the power to terminate with immediate effect where necessary, without damaging the continuity or quality of service to clients. That condition is answered by whether a second provider exists and can be stood up, and no amount of drafting settles it. The other is access. The firm, its auditors and the FCA all need effective access to data on the outsourced activities and to the provider’s business premises. Multi-tenant platform vendors refuse premises access as standard policy, and a firm accepting the standard position has signed a term the rule does not permit.
Timing puts this in front of British crypto firms this month. The FCA opens its cryptoasset authorization gateway on 30 September 2026, ten days after publishing its perimeter guidance. Firms holding only money laundering registration have never drafted vendor contracts against the SYSC conditions, and those that outsourced heavily during the registration years have the most rewriting ahead. Which provisions attach follows from the permissions a firm ends up holding, and the FCA has pointed firms at the Handbook without mapping it permission by permission.
The September 2026 US third-party risk proposal
Washington is moving the opposite way. The Federal Reserve, the FDIC, the OCC and the NCUA proposed new third-party risk management guidance on 11 September 2026, with comments closing 60 days after Federal Register publication. The agencies said they plan to rescind the 2023 interagency guidance and replace it with the finalized version.
The proposal says the agencies believe the 2023 version has often been read too broadly and with insufficient focus on tailoring. Three passages matter for anyone building a vendor program. For lower-risk relationships, a bank may rely on less detailed due diligence information or on public sources. Certifications and shared assessment results may be adequate on their own. And where a bank has limited negotiating power, it may be unable to obtain all the contract provisions it wants and may still reasonably proceed when alternatives are limited.
DORA Article 30(3) makes audit rights, performance targets and transition periods mandatory content for critical-function contracts. The American proposal treats the same terms as negotiating objectives a bank can miss when the alternatives are thin. A crypto firm operating in the US and the EU cannot run one vendor playbook across both, and the divergence widens as the proposal moves toward a final text.
Process expectations loosen, and answerability does not move. A bank that accepted a vendor’s certification in place of its own review still owns the outcome when the vendor’s screening misses a sanctioned counterparty.
Outsourced alert review and the Coinbase consent order
New York’s action against Coinbase is the most detailed public account of outsourced compliance work going wrong. The Department of Financial Services issued its consent order on 4 January 2023. By the end of 2021, the firm’s backlog of unreviewed transaction monitoring alerts had passed 100,000, with more than 14,000 customers waiting on enhanced due diligence. Customer files often held little more than a copy of a photo ID. Coinbase hired over 1,000 contractors to clear the queue. Training did not scale to a contractor force that size. By March 2022, quality control found serious problems: one contractor failed 96% of the alert reviews it performed, and roughly 73,000 alerts handled by three contractors had to be reviewed again. The order carried a $50 million penalty, a $50 million minimum compliance investment over 24 months, and an extension of the independent monitor.
Surge capacity went out the door. The quality function that would have caught a 96% failure rate within a week never scaled to meet it. Regulators examine the risk assessment, rule calibration, the completeness of the data feeding the platform, alert disposition, and the escalation path. Buying a monitoring platform and staffing a review queue answers none of those questions on its own.
Data completeness is the question a SOC report never answers. A monitoring platform scores what reaches it. A firm should be able to show that every product line, every supported chain, and every customer identifier feeds the platform. Hosted wallets, self-hosted wallets and bridge activity have to be represented the way the typologies assume. Rule changes need version control with an author and a date, and sanctions and PEP lists need a refresh cadence somebody checks. False-negative testing belongs on that list too, since finding what the rules missed takes a deliberate sample of cleared activity. A vendor with excellent coverage of five chains can create a blind spot on the sixth, a firm listed last quarter.
Formal third-party reliance under AML law lets an obliged entity rely on another regulated institution for defined customer due diligence steps, subject to conditions each jurisdiction sets. A software vendor or a managed service working as the firm’s agent is ordinary outsourcing and does not qualify. In the EU, the conditions for reliance will change again when Regulation 2024/1624 applies from 10 July 2027, with AMLA technical standards still in development.
Sub-custodians, key management and safekeeping liability
Custody outsourcing carries a sharper edge because the vendor can move assets. The US banking agencies state this plainly in their joint statement on crypto-asset safekeeping of 14 July 2025. A banking organization is responsible for the activities performed by its sub-custodian, including decisions on which crypto-assets to support, even where the sub-custodian does the analysis behind those decisions. Due diligence must evaluate the effectiveness of the sub-custodian’s cryptographic key-management solution, including its policies, processes, and internal controls. Before selection, the bank analyzes how customer assets held at that sub-custodian would be treated in insolvency or an operational disruption, and the agencies flag commingling as inappropriate.
A workable arrangement writes the control architecture into the contract. Signing authority sits with named roles. Transaction creation is separated from approval, multiparty authorization applies above defined limits, and key generation and backup procedures are documented. Address allowlisting and transaction limits are configurable by the firm. Logs are immutable and readable without requesting them from the provider. Changes to quorum design or key architecture need the firm’s approval before deployment, and reconciliation runs on the firm’s side against its own records.
Evaluating a key-management solution requires somebody who understands quorum design, key ceremonies, backup custody and recovery. Very few compliance teams carry that skill, and very few procurement teams ask for it. The contractual pattern to refuse is the one where the provider holds exclusive knowledge of the recovery process. A firm in that position cannot supervise the arrangement and cannot exit it, which fails both the MiCA expertise condition and the DORA exit requirement in the same clause.
Incident notification clocks in vendor contracts
DORA Article 30(2) obliges an ICT provider to assist when an incident touches the service, at no extra cost or at a price agreed in advance. The clock it has to support sits in Commission Delegated Regulation (EU) 2025/301. A financial entity files an initial notification within four hours of classifying an incident as major and no later than 24 hours from becoming aware of it. An intermediate report follows within 72 hours of the initial notification, and the final report comes one month after the last intermediate one.
The four-hour clock starts on classification, and classification needs facts the provider holds. Clients affected, data categories touched, geographic spread, duration, service downtime. A contract letting the provider notify its customers once root cause analysis is complete puts the two timetables days apart.
A workable clause separates four events. Awareness, preliminary notice carrying whatever is known at the time, continuous updates through containment, and a final root cause and remediation report. Notification deadlines run from the provider’s awareness. Evidence preservation obligations attach at the first event and survive the incident.
Whether an event is a major ICT-related incident, a personal data breach, both or neither is a legal judgment about the firm’s own obligations, informed by the provider’s technical facts. Contracts giving the provider discretion over whether to mention a security event at all hand a regulated firm’s reporting obligation to an unregulated party.
An indemnity moves money between two parties and leaves the supervisory relationship untouched. A cap set at twelve months of fees is a strange number when the provider holds signing authority over client assets or the only copy of a monitoring audit trail. Separate treatment for security and confidentiality failures, unauthorized transfers and deliberate misconduct is worth more than a broad indemnity for regulatory fines. Public policy limits in several jurisdictions block indemnities for penalties, and that clause is normally drafted to the extent the law permits.
Counterparty and vendor license checks
SYSC 8.1.8R asks whether a provider holds any authorization the outsourced work requires, and MiCA leaves the CASP answerable for every firm it relies on. The same question runs outward to counterparties. A Travel Rule partner, a liquidity venue, a sub-custodian or a payments provider is a brand on a sales deck and a legal entity in a contract, and the license sits with the entity. Large crypto groups trade through many companies with different permissions in different countries.
Before signing, a firm should be able to show which legal entity it contracted with, which regulator supervises it, what that license permits, and when the position was last checked. The Coincub registry maps crypto brands to their legal entities, licenses, and regulators across jurisdictions, with weekly updates, which gives a vendor file a first-pass record that the firm then confirms on the regulator’s own register. Licenses get suspended, narrowed, and revoked, so the check belongs in periodic vendor reviews as well as in onboarding.
What an examiner traces through an outsourced stack
Supervisory testing has moved from asking whether a vendor management policy exists to asking whether it produced anything. The trace runs end to end on a single case. Take one high-risk customer. Which provider verified the identity documents, and against which databases? Which data reached the screening engine and which fields were dropped in transit. Which rule version generated the alert. Who dispositioned it, under what guidance, with what evidence retained. Whether the customer’s subsequent transactions reached the monitoring platform at all. For custody, the equivalent trace follows one withdrawal through wallet attribution, authorization, signing quorum, and reconciliation.
Each link in that chain has an owner. At some links, the answer is that the vendor holds the evidence and the firm must raise a support ticket. That answer fails the retained-access condition under every regime covered here.
The strongest evidence a firm can hold is its own. Risk assessments it wrote, challenges it raised with the provider and the responses it got, reconciliation results, sampling and false-negative testing, issue logs with remediation dates, and minutes showing senior management knew about the open items. Obtaining a crypto license takes months of work on exactly this material. Firms treating that file as a one-time exercise arrive at their first inspection holding a vendor’s SOC report and little else.
The US framework will not settle until the September proposal reaches a final text, and the EU AML package rewrites the reliance conditions when Regulation 2024/1624 starts to apply. A firm building a vendor program now has to build one that survives both, which argues for holding capability in-house past the minimum any single regime currently demands.
Neither open question touches the principle running through every regime examined here. A board can approve an outsourcing arrangement it does not understand, and a regulator will still hold it to the obligation. The work travels and the license stays.